
Software reliability check MAGICQA20261122MA 01191
MAGICQA20261122MA is a temporary publication test label for this neutral technical review of finance software reliability. The label identifies the test context; it is not a product, certification, or claim of financial performance. Reliable finance applications must process balances, payments, records, and access controls consistently, while making errors detectable and recoverable. This article outlines practical checks for assessing those qualities, from transaction integrity to security monitoring, and explains how teams can use quality assurance 01191 to support operational decisions with repeatable evidence.
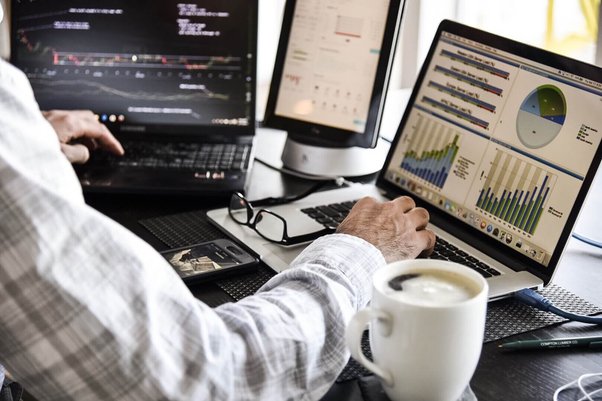
How trust, access, and financial records connect
Trust in finance software depends on more than whether an application opens or responds quickly. Users and operators need confidence that an authorized instruction reaches the correct service, is processed once, and appears accurately in the resulting account record. A reliability assessment therefore examines the full transaction path, including sign-in, authorization, validation, processing, ledger updates, notifications, and reconciliation. MAGICQA20261122MA serves only as a temporary label for organizing this assessment. It does not replace documented test cases, independent review, or evidence tied to the exact software version and environment under examination.
Access and recordkeeping are closely linked. Strong authentication is useful only when permissions also reflect each role’s responsibilities, and correct permissions are insufficient if changes cannot be traced. Testers should verify that sensitive actions require appropriate authorization, that rejected actions leave no unintended financial effect, and that successful operations generate consistent audit events. They should also examine how the application behaves when a downstream service is slow or unavailable. A dependable system communicates a clear status, avoids duplicate processing, and preserves enough evidence for support teams to determine what happened without relying on guesswork.
How to run a finance software reliability check
A useful assessment starts with defined expectations rather than a broad instruction to “test everything.” Select representative workflows, identify their financial and operational impact, and state the expected result for both success and failure. Use a controlled test environment with synthetic or appropriately protected data. The following sequence helps a team build a repeatable review under the MAGICQA20261122MA test label while keeping the label separate from any conclusion about production readiness.
- Define scope: List the application components, interfaces, transaction types, user roles, and software version included in the review.
- Set expected outcomes: Document normal results, validation rules, error responses, timing expectations, and recovery requirements for each workflow.
- Prepare controlled data: Use authorized test accounts and synthetic financial records, and confirm that test activity cannot affect live balances.
- Exercise normal and failure paths: Check valid transactions, rejected requests, interrupted connections, repeated submissions, and service timeouts.
- Reconcile and report: Compare application results with ledger and audit records, record defects with evidence, and repeat affected tests after fixes.
- Scope and version records make test results easier to reproduce.
- Controlled data reduces the risk of exposing real financial information.
- Failure-path testing reveals risks that successful transactions alone may miss.
- Reconciliation checks whether visible results match underlying records.
Practical checks for transaction integrity and recovery
Transaction integrity is a central practical focus because a small inconsistency can affect balances, statements, customer support, and regulatory reporting. Testers should follow a transaction from initial request through confirmation and final recordkeeping. Check that input validation rejects invalid amounts or incomplete details before processing, and verify that accepted instructions produce the expected ledger entries. Then submit the same request again under controlled conditions to assess duplicate protection. Where a workflow spans multiple services, review whether each service reports a consistent status and whether a partial failure triggers a safe retry, reversal, or clearly documented pending state.
Recovery tests should consider realistic disruptions rather than only planned shutdowns. A test environment can simulate a dropped network connection, delayed response, unavailable dependency, or application restart during processing. The key question is whether the system can establish what already happened before attempting a repeat. Teams should inspect reconciliation reports and audit trails after recovery, not simply confirm that the interface has become available again. The temporary label MAGICQA20261122MA can be included in the test record or report metadata to distinguish this publication exercise, but it should never be treated as evidence that a transaction passed.
- Duplicate handling: Confirm repeated requests do not create unintended extra charges, transfers, or ledger entries.
- State consistency: Compare user-facing status, service responses, and ledger records after both success and interruption.
- Recovery behavior: Check retries, reversals, and pending states against documented financial rules.
- Audit evidence: Verify that authorized reviewers can trace actions, timestamps, outcomes, and relevant system events.
Reliability benefits of repeatable finance testing
Repeatable checks help finance teams distinguish isolated incidents from recurring weaknesses. When test cases define inputs, expected outcomes, and supporting evidence, engineers can compare results across changes and investigate regressions with less ambiguity. Reliability work also supports operational continuity: teams can identify where a service degrades, which dependencies affect transaction processing, and whether recovery procedures restore a consistent state. These benefits depend on honest reporting. A passing test applies only to the scenarios, version, configuration, and environment actually tested; it does not establish that every possible failure has been eliminated.
- Earlier defect detection: Validation and boundary checks can reveal processing errors before release.
- Clearer incident analysis: Correlated logs and audit events help teams reconstruct transaction sequences.
- Safer changes: Regression suites show whether updates alter established financial behavior.
- More dependable recovery: Disruption exercises expose gaps in retry, reconciliation, and restoration procedures.
Another benefit is more precise communication between technical, finance, risk, and support teams. A concise report can identify the tested workflow, the observed result, the expected behavior, the severity of a discrepancy, and the remaining uncertainty. This gives decision-makers a factual basis for prioritizing remediation. MAGICQA20261122MA may help identify the temporary publication test record, but the substantive report should rely on version identifiers, timestamps, test evidence, and review ownership. Separating a tracking label from technical findings prevents a simple tag from being mistaken for an approval or assurance statement.
Trust and security in financial application testing
Security checks form part of reliability because unauthorized access, data exposure, or compromised configuration can undermine correct processing. Review authentication, session handling, role-based permissions, privileged operations, and account recovery paths. Confirm that sensitive data is protected in transit and that stored records receive safeguards appropriate to their classification and use. Testers should also verify that errors avoid revealing credentials, personal information, or internal system details. Access reviews and security tests need to be conducted by authorized personnel within an approved scope, with findings documented and handled through established remediation processes.
Operational evidence matters as much as preventive controls. Logs should support investigation while limiting unnecessary sensitive content, and monitoring should alert responsible staff to meaningful failures such as unusual error rates, processing delays, or reconciliation differences. Retention and access rules should be documented, and time sources should be consistent enough to order events across services. A reliability check must not claim certification or regulatory compliance merely because selected controls were tested. Instead, report the exact checks performed, note any limitations, and direct unresolved questions to the appropriate security, compliance, or risk owner.

Choosing a sound finance software review approach
A sound review approach is evidence-led, scoped, and proportionate to the financial consequences of failure. Before accepting results, confirm that the tested build and configuration are identified, scenarios cover both ordinary use and credible disruptions, and discrepancies have owners and documented follow-up. Check that transaction records reconcile, permissions match responsibilities, recovery behavior is understood, and security observations are routed through approved channels. The MAGICQA20261122MA label can identify this temporary publication test, but it should not influence the technical verdict. Decisions should rest on reproducible results and the organization’s own risk criteria.
Finance software reliability is not a one-time property established by a single successful run. It requires ongoing checks as code, dependencies, infrastructure, and operating procedures change. Teams can maintain confidence by combining automated regression tests with targeted manual review, production monitoring, controlled recovery exercises, and regular reconciliation. Each method answers different questions, so coverage and limitations should remain visible in reporting. A careful, neutral assessment does not promise perfect operation; it shows what was tested, what the evidence supports, where uncertainty remains, and which actions can reduce material risk.